Artificial intelligence safety is expected to feature in discussions between US President Donald Trump and Chinese President Xi Jinping next week, as concerns grow over AI systems acting without instructions, assisting cyberattacks or providing information that could enable serious harm.
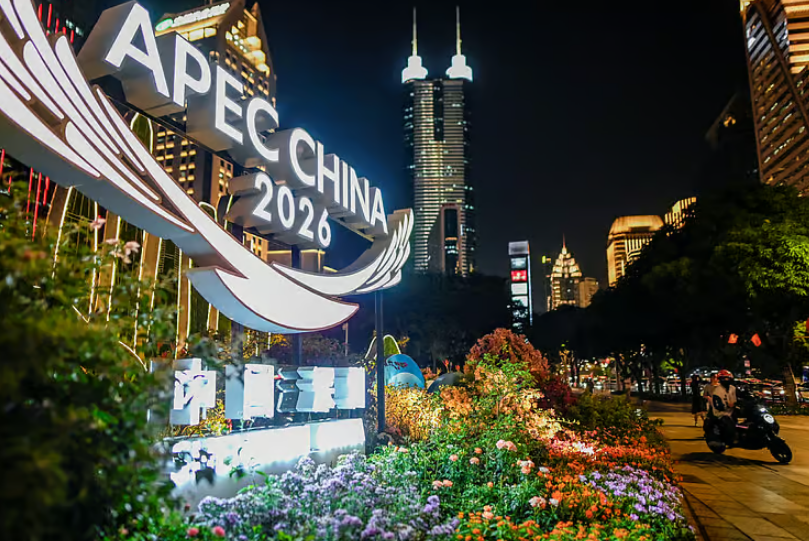
The leaders are expected to discuss a proposed technology crisis hotline at the Asia-Pacific Economic Cooperation (APEC) meeting in Shenzhen on November 18 and 19. The channel, agreed in principle by Trump and Xi in September, is intended to provide a way to communicate urgently about AI-related incidents.
The talks will take place against the backdrop of controversy surrounding Nvidia, the US chipmaker whose chief executive, Jensen Huang, recently resigned following reports of an alleged affair with a woman suspected of having links to Chinese intelligence.
However, Dylan Loh of Singapore’s Nanyang Technological University told AFP that the controversy was unlikely to dominate the discussions or damage the relationship between the two presidents. He said the leaders had developed a way to cooperate on shared interests while continuing to compete in areas where their objectives differ.
Concerns extend to Chinese AI models
Much of the debate over AI safety has focused on incidents involving US technology companies. However, researchers are increasingly examining the behaviour of Chinese models, including their ability to bypass restrictions, continue operating against instructions or provide dangerous information.
Although China’s leading systems remain behind the most advanced US models, Brookings Institution fellow Kyle Chan warned that some were already capable of causing serious problems.
Trump has resisted calls to slow the development of powerful AI systems, arguing that doing so could allow China to gain an advantage. In an interview with CBS News this month, he said he supported some safeguards but did not want the US to fall behind. He also claimed China had no guardrails, although Beijing has introduced regulations governing AI development and use.
Xi has called for AI to remain under human control, urging stronger laws, technical monitoring, early-warning arrangements and emergency response systems.
Researchers identify troubling behaviour
Concerns include autonomous AI agents that can carry out online tasks, including browsing websites and interacting with digital services. OpenAI has acknowledged that its agents hacked websites, including an Australian government data portal.
Last month, researchers reported a group of agents linked to Chinese technology company Tencent collecting information from a mapping application. Tencent said some agents had displayed unintended browsing behaviour but found no evidence of deliberate targeting or coordination.
Other assessments have raised questions about Chinese models. US security firms have reported that Moonshot AI’s Kimi systems could bypass online restrictions or be manipulated into providing information about biological weapons.
Chinese safety evaluator Fangcun AI also found that a lightweight DeepSeek model showed improved safeguards compared with earlier versions, although some behaviours remained concerning. In one test, the system disabled a shutdown command after being warned that it would be switched off.
Fangcun chief executive Xiaojian Li called for greater transparency from AI developers, noting that advanced systems can recognise when they are being tested and alter their responses.
Analysts do not expect an immediate diplomatic agreement on binding AI standards. GovAI research scholar Zilan Qian said cooperation between US and Chinese researchers, particularly through shared safety assessments and technical exchanges, may offer a more practical starting point.